Car Hacking Village·26 min
Yago Lizarribar
Reveals how unencrypted RF broadcasts from direct Tire Pressure Monitoring Systems (TPMS) enable vehicle tracking and custom message injection to spoof ECUs.
automotivetpmsrf+2
64 talks tagged with this topic.
Loading filters…
1–24 of 58 talks / 64 · loading…
Car Hacking Village·26 min
Yago Lizarribar
Reveals how unencrypted RF broadcasts from direct Tire Pressure Monitoring Systems (TPMS) enable vehicle tracking and custom message injection to spoof ECUs.
Creator Stage·38 min
Federico Lucifredi
Tutorial on keyboard attack vectors, ranging from hardware keyloggers and Van Eck phreaking electromagnetic emanations to acoustic typing eavesdropping.
Main Stage·43 min
Erwin Karincic · Woody
Discloses cryptographic and firmware vulnerabilities in goTenna Pro mesh networking devices, allowing off-grid key extraction and message decryption.
Main Stage·23 min
Andrew Logan
Demonstrates how real-time AI voice cloning and software-defined radios can inject fraudulent air traffic control clearances on unencrypted VHF frequencies.
RF Village·25 min
Allan Riordan Ball
Allan Riordan Ball demonstrates bypassing SSIDs, handshakes, and IP stacks to sling raw 802.11 frames with Scapy as a peer-to-peer data transport pipe.
RF Village·40 min
Dan Perret
Explains how the RF Village Capture the Flag team designs wireless challenges and automates over-the-air signal transmission using challengectl.
RF Village·47 min
Manuel Rabid
Analyzes the VHF Weather Radio SAME protocol and seismic alert systems (SASMEX), demonstrating how unauthenticated broadcast signals risk false alarms.
RF Village·43 min
Exploding Lemur
Breaks down radio frequency fundamentals, antenna physics, filters, Shannon-Nyquist modulation theories, and Software-Defined Radio architectures for beginners.
Security Fest·39 min
SecurityFest 2019 explores Himanshu Mehta - RF Exploitation! Demystifying IoT OT hacks with SDR.
Videos·39 min
Nitin Lakshmanan · Sunil Kumar
Industry experts analyze emerging threats surrounding Practical Exploitation Of Zigbee Networks With RF Transceivers by Nitin Lakshmanan & Sunil Kumar.
Creator Stage·22 min
Ken Munro
Analyzes how GPS coarse time spoofing invalidates digital certificates on aircraft, grounding fleets and disrupting avionics communications.
Creator Stage·27 min
D. Erazo
Demonstrates hardware analysis of an automotive key fob using a logic analyzer and HackRF to clone unprotected learning code RF signals.
Creator Stage·26 min
G. Longo · V. Lenders
Demonstrates practical RF attacks against TCAS II collision avoidance systems to forge resolution advisories and disable collision detection.
Creator Stage·24 min
Matt Thomassen · Sean McKeever
Analyzes airborne Wi-Fi signal propagation and reconnaissance data collected by warflying a small Cessna aircraft at various altitudes.
Hack In The Box Security Conference·53 min
Marc Newlin
Marc Newlin examines #HITB2016AMS CommSec Track D1 - Applying Regulatory Data to IoT/RF Reverse Engineering.
Main Stage·45 min
Romain Cayre · Damien Cauquil
Framework and unified protocol architecture for wireless security research, hardware abstraction, and over-the-air exploitation.
Main Stage·43 min
Erwin Karincic · Woody
Reverse engineering and RF exploitation of goTenna Pro encrypted mesh communication radios used in tactical environments.
Main Stage·41 min
David Melendez · Gabriela Garcia
Explores implementing low-cost frequency-hopping spread spectrum algorithms on DIY and consumer drones to resist RF jamming and anti-drone interception.
Main Stage·38 min
Joseph Gabay
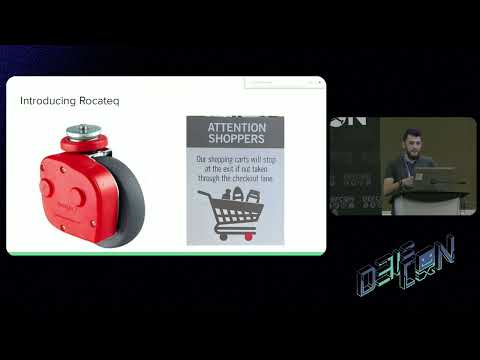
Reverse engineers electronic shopping cart containment wheels, capturing ultra-low-frequency and 2.4 GHz RF signals to unlock wheel braking mechanisms.
RSAC Cybersecurity·10 min
Security researchers examine technical aspects of Quick Look: RF Exploitation: IoT and OT Hacking with Software-Defined Radio.
RSAC Cybersecurity·45 min
Engineers explore architecture and security mechanisms for RF Exploitation: IoT and OT Hacking with Software-Defined Radio.
War Stories·38 min
Paz Hameiri
Paz Hameiri develops a simulation framework to spoof and jam weather balloon radiosonde telemetry, threatening global climate models and rocket launches.
Car Hacking Village·40 min
Ayyapan Rajesh
Ayyapan Rajesh details CVE-2022-27254, demonstrating how unencrypted fixed rolling codes in Honda remote keyless entry systems allow replay and vehicle theft.
DCGVR Village·25 min
Demystifying amateur radio for modern hackers, exploring digital packet radio, APRS telemetry, SDR integration, and emergency communications.