Source of Truth - A Field Guide for Deep Technical Research
Where
OWASP
DEF CON 34
Duration
16 min
Presents a method for researching protocols and standards, tracing claims back to primary sources and spotting the assumptions that shape a design.
Summary
The talk starts from a common problem in security work: one reasonable question about a protocol quickly becomes a pile of browser tabs, outdated blog posts and simplified architecture diagrams. The speaker's example was learning OAuth under time pressure, where the first popular article was not enough. The core point is that the original standards hold the detail that summaries leave out, and that they link to a connected set of companion documents rather than standing alone.
The middle of the talk describes a research workflow. The speaker looks for the RFCs and their related best current practice and threat model documents, which were written for an earlier client-server world and can differ from how single-page applications work. Questions are treated as hypotheses to test, such as whether JavaScript can reach a token, and each token or data transfer is traced to find where leaks tend to happen, usually at the public internet boundary. AI tools are used with caution: they can produce citations that do not resolve, so they are best used to summarize sources the researcher has already read.
The takeaway is to decide identity and cryptography questions early, since these areas are often left unowned. Standards such as the OWASP ASVS can be attached to project stories and acceptance criteria, and large decisions can be broken into small steps to avoid analysis paralysis. The speaker also notes that the authors' own documents, not secondary articles, are the better guide to what a design should guarantee.
Materials
Related talks
Main Stage·15 min
Samet Tasci · Mehmet Key
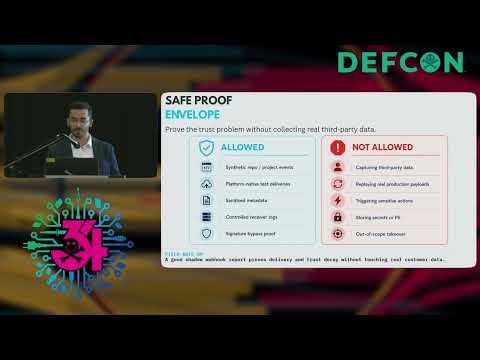
Shows how forgotten SaaS webhooks can leak event data or accept forged messages, and how to turn them into reproducible bug bounty reports.
Payment Village·42 min
Jorge Braniff · Sanjeev Sharma · Monique Garcia · Daniel Cuthbert
Panelists from payments, fraud and security research discuss how AI agents will reshape buying, fraud risk, identity checks and trust in payments.
Voting Village·28 min
John Odum
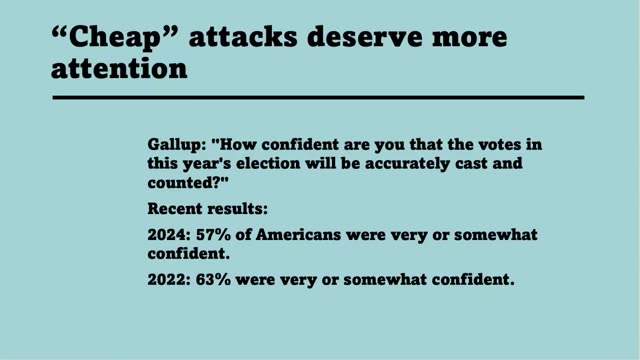
Shows how cheap, low-skill attacks such as website defacement, malicious voting apps, and phone-based misdirection could erode voter confidence in internet voting.