CyberRisk TV·17 min
Matthew Warner
Matthew Warner explores Blumira's Vision: Security Built for MSPs & SMBs.
blumiravisionbuilt+3
14 talks tagged with this topic.
Loading filters…
1–13 of 13 talks / 14 · loading…
CyberRisk TV·17 min
Matthew Warner
Matthew Warner explores Blumira's Vision: Security Built for MSPs & SMBs.
Ekoparty Security Conference·42 min
Ochoa · Azubel
Presents ochoa & Azubel - Understanding the Win SMB NTLM weak nonce vulnerability and evaluates key implications for security practitioners.
HITCON·56 min
Nicolas Joly
Engineers explore architecture and security mechanisms for [HITCON CMT 2017] R0D203 - Nicolas Joly - Mitigating the unknown, when your SMB exploit fails.
Wild West Hackin' Fest·49 min
Amanda Berlin
Security researchers examine technical aspects of A Post Incident Case Study for SMB Response Teams | Amanda Berlin.
ROOTCON·17 min
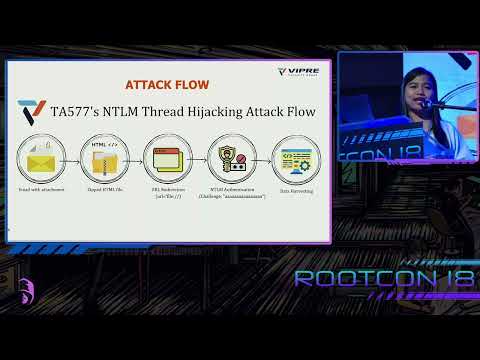
Evaluates TA577 Tactics: NTLM Hash Theft Through SMB Thread Hijacking by: Marianne Bermejo and evaluates key implications for security practitioners.
RSA Conference (RSAC)·47 min
Presenter: Tarah Wheeler
Demonstrates future Proofing SMBs for the Evolving Global Compliance Landscape and evaluates key implications for security practitioners.
RSAC Cybersecurity·40 min
Security researchers examine technical aspects of In the Crosshairs: The State of Security in SLTT and SMB Organizations.
RSAC Cybersecurity·1 hr 7 min
Engineers explore architecture and security mechanisms for What SMBs Need to Know to Survive a Ransomware Attack.
FRSecure·1 hr 1 min
Engineers explore architecture and security mechanisms for UNSECURITY Episode 126: Reactions to "15 Security Pitfalls and Fixes for SMBs".
Main Stage·24 min
droogie
Revives Windows null session attacks against modern Active Directory environments, demonstrating significant unauthenticated enumeration capabilities.
Main Track 1·37 min
Gil Cohen
Named pipes as application-level entry vectors for buffer overflows, DoS, and code injection attacks.
Main Stage·25 min
Tim Mullen
Tim Mullen examines dEF CON 9 Abstract and Bio Missing from the speaker’s page archive.
Main Stage·31 min
Mr. Nasty
Mr. Nasty explores using tools to obtain recon on nt networks at DEF CON 8, examining windows-nt and practical defenses.