DragonJAR - Hacking y Seguridad Informática·2 hr 15 min
Details ¿Cómo usar Metasploit? - Curso GRATIS de Introducción a Metasploit 2021 and evaluates key implications for security practitioners.
metasploitusarcurso+2
17 talks tagged with this topic.
Loading filters…
1–17 of 17 talks · loading…
DragonJAR - Hacking y Seguridad Informática·2 hr 15 min
Details ¿Cómo usar Metasploit? - Curso GRATIS de Introducción a Metasploit 2021 and evaluates key implications for security practitioners.
DragonJAR - Hacking y Seguridad Informática·42 min
Examines RID Hijacking in Windows (metasploit rid_hijack) and evaluates key implications for security practitioners.
Eye on Tech·11 min
Analysts investigate attack surfaces and defenses concerning A Metasploit Framework Walk-Through for Beginners.
hardwear.io·46 min
Industry experts analyze emerging threats surrounding 2017:- Latest Metasploit Hardware Bridge Techniques by Craig Smith.
TROOPERS IT Security Conference·48 min
Craig Smith
Craig Smith examines TR17 - Metasploit Hardware Bridge Hacking.
CypherCon 7.0·51 min
Randy Lee | CypherCon 7.0
Randy Lee | CypherCon 7.0 examines Mastering Metasploit: Advanced Techniques and Demos.
DEFCON Switzerland·49 min
Philipp Schroedel · Max Moser
Industry experts analyze emerging threats surrounding #days: Philipp Schroedel & Max Moser - CARAT: Metasploit Config & Risk Assessment Tool.
BSidesCharm·53 min
2026 - New Windows Persistence Techniques in Metasploit.
CarolinaCon·44 min
Ryan Linn
Getting Shells When Metasploit Fails - Ryan Linn.
PancakesCon·46 min
Tina Coleman
4 - Tina Coleman - Playing with Exploits in Metasploit & Playing with Ideas via Clowning.
Aerospace Village·28 min
Pearce Barry
Pearce Barry revives hardware bridging tools in Metasploit, connecting CAN bus and serial hardware interfaces directly into avionics attack surfaces.
Main Track 1·32 min
JoSh Pitts
Bypassing EMET and exploit mitigations to create improved Metasploit shellcode payloads.
Village Presentations·1 hr 23 min
Catatonic
Catatonic details the responsible disclosure of vulnerabilities in the Hak5 WiFi Pineapple and demonstrates 'Tospo', a self-replicating wireless worm.
Main Stage·28 min
Nadeem Douba
Nadeem Douba explores sploitego - maltego's (local) partner in crime at DEF CON 20, examining metasploit and practical defenses.
Main Stage·39 min
Matthew Toussain · Christopher Shields
Matthew Toussain and Christopher Shields details copy of the slides for this talk are here:.
Main Stage·33 min
David Maloney
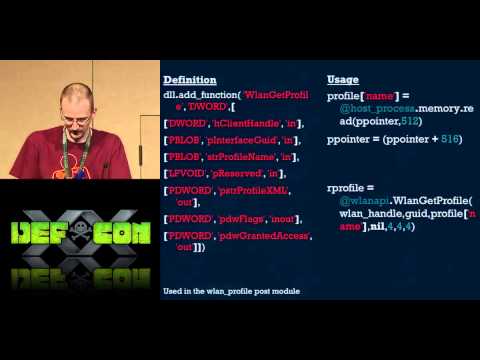
David Maloney explores weaponizing the windows api at DEF CON 20, examining metasploit and practical defenses.
Main Stage·31 min
Paul Haas
Paul Haas explores advanced format string attacks at DEF CON 18, examining metasploit and practical defenses.