The Linux Foundation·32 min
Nikunj Doshi · PDT Corp.
Outlines container Escape Paths Nobody Monitors: Abusing Linux Debug Interfaces and evaluates key implications for security practitioners.
linuxcontainer-escapecontainer+2
13 talks tagged with this topic.
Loading filters…
1–13 of 13 talks · loading…
The Linux Foundation·32 min
Nikunj Doshi · PDT Corp.
Outlines container Escape Paths Nobody Monitors: Abusing Linux Debug Interfaces and evaluates key implications for security practitioners.
Hack In The Box Security Conference·43 min
Li Qiang
Li Qiang details #HITB2021SIN D2T2 - Container Escape In 2021.
OWASP Global AppSec San Francisco·45 min
Amit Schendel
Reviews the Container Escape Room: An Exploration of Container Escapes and evaluates key implications for security practitioners.
RSA Conference (RSAC)·31 min
Presents container Escape: All You Need Is Cap (Capabilities) and evaluates key implications for security practitioners.
Black Hat USA 2022·36 min
Provides kubernetes Privilege Escalation: Container Escape == Cluster Admin and evaluates key implications for security practitioners.
Main Stage·44 min
Billy Jheng · Muhammad Ramdhan
Billy Jheng and Muhammad Ramdhan demonstrate multiple novel container escape vectors in Google Kubernetes Engine (GKE) to achieve host node takeover.
Main Stage·32 min
Samuel Erb · Justin Gardner
Samuel Erb and Justin Gardner share the story of finding and exploiting a complex RCE exploit chain against KASM Workspaces streaming software.
Main Stage·39 min
Eran Segal
Eran Segal investigates Windows container isolation (Process Isolation & Hyper-V), demonstrating novel container escape techniques via Silo IPC mechanisms.
Main Stage·43 min
Aviv Sasson
Aviv Sasson presents the complete technical breakdown of FabricEscape (CVE-2022-30137), breaking out of Linux containers to seize full Azure Service Fabric cluster control.
Main Stage·36 min
Aviv Sasson
Aviv Sasson details discovering FabricEscape, a severe vulnerability in Microsoft Service Fabric allowing unprivileged containers to seize full cluster admin rights.
Cloud Village·16 min
Yuval Avrahami
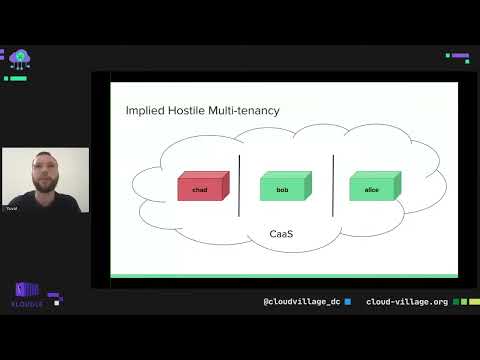
Palo Alto Networks researcher Yuval Avrahami presents WhoC, a container image tool that extracts the underlying container runtime in public CaaS clouds.
Cloud Village·35 min
Daniel Prizmant
Daniel Prizmant demonstrates fundamental architectural security flaws in Windows Server Process-Isolated Containers, executing root container escapes.
Main Stage·42 min
Ian Coldwater · Chad Rikansrud
Ian Coldwater and Chad Rikansrud unite container and mainframe hacking to achieve the world's first container escape on an IBM LinuxONE mainframe.