Securing Confidential VMs with COCONUT-SVSM
Jörg Rödel explores Securing Confidential VMs with COCONUT-SVSM.
Summary
COCONUT-SVSM Overview
SUSE maintainer Joerg Roedel introduces the open-source COCONUT Secure VM Service Module, a platform for secure hypervisor services in confidential VMs. Started as a 2022 prototype, it booted Linux guests in CVMs by early 2023, gained filesystem support, multitasking, TPM emulation, CI testing, 23 contributors, and Confidential Computing Consortium onboarding.
Confidential VM Threat Model
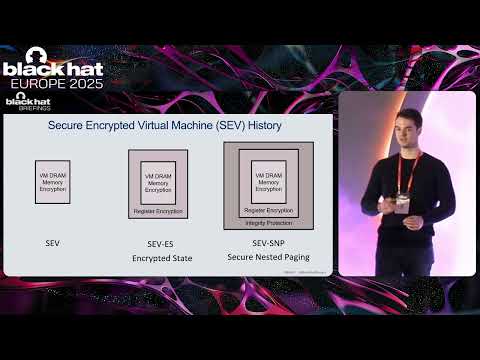
Untrusted hypervisors normally manage guest memory, intercepts, interrupts, and device emulation— exposing data and register-state attacks. Hardware extensions (AMD SEV-SNP, Intel TDX, Arm CCA, RISC-V CVME) encrypt memory and detect remap/replay tampering; some intercepts trap into guest kernels instead of the host.
SVSM’s Role
Where hardware cannot fully mitigate hypervisor functionality, guest-side code can absorb tasks. COCONUT-SVSM implements services that complement hardware protections on x86 and analogous architectures, extending confidential computing beyond raw memory encryption toward practical guest-controlled security modules.
Related talks

Black Hat Europe 2025·40 min
Jesse De Meulemeester · Jo Van Bulck · David Oswald
Security researchers examine technical aspects of Low-Cost Memory Interposer Attacks On Confidential Computing.
Black Hat Europe 2025·35 min
Benedict Markus Schlüter
Security researchers examine technical aspects of RMPocalypse: A Catch-22 Breaking AMDs Confidential Computing.

hardwear.io·52 min
Presenters detail vulnerability discovery and exploitation in Securing The Unseen: Vulnerability Research In Confidential Computing by Josh Eads and Cfir Cohen.