There's A Bug in My Boot Finding Vulnerabilities in U Boot
Where
Packet Hacking Village
DEF CON 34
Duration
35 min
Shows how to find bootloader bugs in U-Boot by mining patch history, writing CodeQL queries, and generating malformed SquashFS images to fuzz a native sandbox build.
Summary
Bootloaders sit at the base of embedded systems, often lack modern exploit mitigations, and run in routers, medical devices and industrial equipment. Their updates rarely reach deployed hardware, so bugs found early matter. The talk maps U-Boot's attack surface, which centers on file system parsing and its built-in TCP/IP stack, and points to past storage-related CVEs showing recurring off-by-one and integer overflow patterns in symlink and inode handling.
The speaker explains why conventional approaches are costly. Emulation through QEMU or rehosting struggles with peripherals, and hardware-in-the-loop does not scale. Instead, the work mined U-Boot mailing-list patches for overflow fixes that never received a CVE, then used CodeQL-style queries to search for the same pattern still present elsewhere in the code. Local language models were used to generate malformed SquashFS images, checked with GDB and callgrind to confirm the intended code paths were reached. A fuzzing script then produced 100 random images, one of which crashed U-Boot's sandbox build on an ordinary x86 laptop. The same bug reproduced on a BeagleBone Black, and a related crash appeared in another bootloader.
The takeaways are practical: mine patch history for bug patterns, use a native sandbox build with sanitizers for file system parsers, and treat LLMs as helpers for crafting structured malformed inputs when paired with a tight harness. The speaker also notes that the attacker-controlled file system threat model limits some findings.
Materials
Related talks

IoT Village·40 min
Andrew Bellini
Shows how a beginner can use AI agents and a cheap bench rig to find and exploit bugs in consumer IoT firmware, using a router as the example.

Payment Village·18 min
Chaio-Lin Yu
Shows how a nine-dollar payment terminal fell to a three-bug chain over Wi-Fi, giving unauthenticated access and then root on a certified production unit.
Packet Hacking Village·42 min
Tony Martin · Arie Haenel
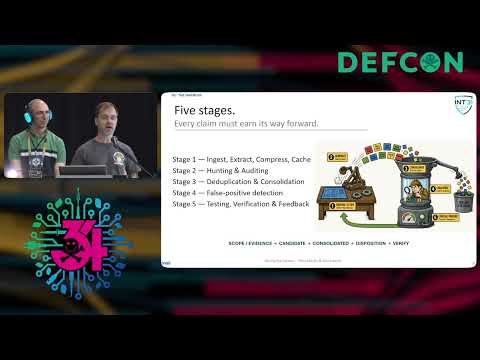
Presents a five-stage harness that pairs frontier models with scoping, retrieval, deduplication and exact-tool checks to cut false positives in LLM vulnerability hunting.