NTLMv1 SSP DES Mechanics Explained
Where
Talks
ShmooCon 2024
Duration
10 min
Explains how NTLMv1 challenge responses are built from DES keys and shows them cracked into domain controller hashes.
Summary
The talk opens with coercion. The speaker starts from a low-privilege domain account and makes a domain controller authenticate to his machine, which is running Responder to catch the hash. The capture is an NTLMv1 challenge response, and the speaker points out that older rainbow-table approaches stop working once the client challenge is modified by the extended session security setting. He then uses his own Python tool to split the response into its parts.
The middle of the talk covers the mechanics. The NT hash is divided into three seven-byte chunks, each padded and used as a DES key to encrypt the client challenge. The three ciphertexts are concatenated to form the response. Because of this structure, the attacker cracks three DES keys separately with hashcat mode 14000 and then reassembles them into the original NT hash. In the live demo, the recovered hash is validated against the domain controller machine account and used to dump credentials.
The closing section is about defense and cost. The speaker says the risk comes from the LAN Manager compatibility level being set to 0, 1 or 2, which permits NTLMv1 and leaves no real defense once it is allowed. He estimates the cracking cost at several thousand dollars of GPU time for a few hours of work. Administrators should find the setting in the domain controller security policy and raise it so that NTLMv1 is refused. The talk is mostly a live demonstration.
Related talks
Track 3·18 min
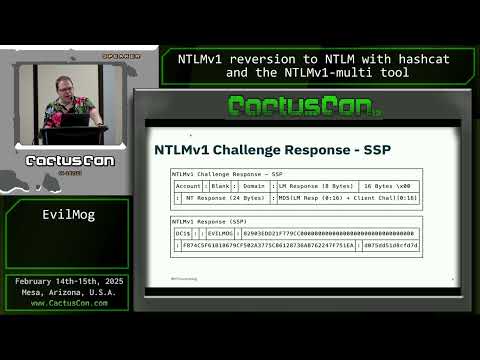
EvilMog
Shows how a captured NTLMv1 challenge response is cracked with hashcat and turned into domain controller NT hashes.
Talks·38 min
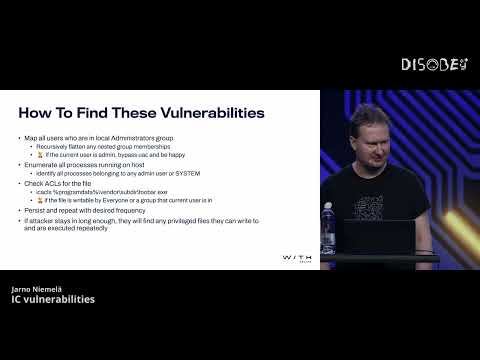
Jarno Niemelä
Shows how misconfigured file permissions in Windows software let a low-privileged user escalate to admin rights.

Talks·27 min
Maxime Escourbiac
Shows how a GlobalProtect client flaw chains from network-level redirection to code execution and then SYSTEM privileges.