NinjaTV: Increasing Your Smart TV IQ Without Bricking It
Felix Leder details ninjaTV - Increasing Your Smart TV’s IQ Without Bricking It Felix Leder DIRECTOR, MALWARE RESEARCH, BLUE COAT NORWAY Smart TVs are growing in popularity.
Summary
Architecture and Background
NinjaTV - Increasing Your Smart TV’s IQ Without Bricking It Felix Leder DIRECTOR, MALWARE RESEARCH, BLUE COAT NORWAY Smart TVs are growing in popularity. Set-top boxes like Apple TV, Roku, or WD TV can make your “normal” TV "smart" and Smart TVs even smarter. Despite their functionality, they’re often missing interesting features, like bit-torrent, VPN and even specific TV channels. This presentation is about how to hack into WD TV set-top boxes and how to add experimental functionality without the risk of bricking it.
Vulnerability Analysis
Whether you want to add exotic TV channels, watch right from bit-torrent, or are crazy enough to do bitcoin mining on your TV – you are in charge. We will demonstrate several methods to become root using everything from remote exploits to hardware hacking. Unfortunately, just becoming root isn’t sufficient to make persistent changes. Because stronger modifications put your device at risk of bricking or of losing specific services, you must dig deeper.
Exploitation and Demonstrations
We are going to present and release our "adjusted" firmware that keeps all the manufacturer's encryption and service DRM keys intact. The firmware is minimally invasive and enables customization without risk. Patching becomes as easy as an SMB software upload. For those who want get deeper and dirtier, we will explain the firmware structure, how to extract the relevant encryption keys, and discuss the protected software modules.
Remediation and Defensive Strategies
This includes a short overview of relevant tools to do hot-patching, live-debugging, and pointers to get started on reverse engineering core applications. Felix Leder leads the mobile threat research at Blue Coat. Taking things apart has been a life time passion for him. His hobbies, like collecting bugs in malware and botnet takeovers, have resulted in successful take-downs of large malicious networks. As a member of The Honeynet Project he is heavily involved in open source security and has been instrumental in developing a number of malware analysis solutions, including Cuckoo box, Norman's Malware Analyzer G2, and Blue Coat's MAA.
Related talks

Main Stage·40 min
Reynaldo · nyx
Reverse engineers commercial vape and sound monitoring sensors installed in school restrooms, uncovering unauthenticated telemetry feeds and cloud vulnerabilities.

Main Stage·42 min
Mark Omo · James Rowley
Reverse engineers electronic gun safes and commercial digital vaults, demonstrating effortless physical and electromagnetic bypasses across leading brands.
Main Stage·40 min
Dennis Giese · braelynn
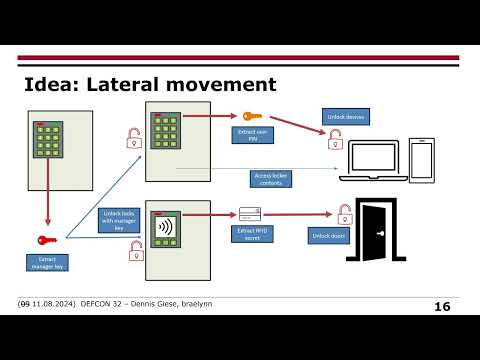
Security evaluation and hardware attack surface analysis of smart electronic lockers and storage cabinets.