Forgotten but Not Gone - Unauthenticated RCEs and LPEs in Legacy Linux Services
Where
Main Stage
DEF CON 34
Duration
35 min
Traces unauthenticated RCE and privilege escalation bugs in GNU telnetd and Samba, showing how decades-old Linux services still hide critical flaws.
Summary
The talk looks at legacy Linux network services that get less attention than newer technology. The speaker starts with an unauthenticated remote code execution flaw in GNU telnetd, disclosed earlier this year after about eleven years. The daemon passes client-supplied environment variables into the command line of the login program, and because those values are not sanitized, an attacker can inject options that skip authentication and return a root shell.
The research then follows the same attack surface to a local privilege escalation. Login trusts a credentials directory variable and a flag file inside it, so a low-privilege user can reach root through telnetd even after the first patch. Turning to Samba, the speaker reports two more unauthenticated RCEs. One comes from a printing interface that places a job name into a shell command. The other comes from a password validation RPC call that reaches a command without escaping. Each issue is shown in a live demo.
The takeaway is that narrow patches fix individual instances but leave the flawed design behind them in place. Practitioners should ask whether a service runs shell commands, sanitizes input, or accepts environment variables from unauthenticated clients, and should not assume that popularity means it has been audited. Printers, routers and other unmanaged devices may still run these daemons unpatched.
Materials
Related talks
Main Stage·37 min
Daniel Hillel · Noam Trobishi
Shows how a use-after-free in the NVIDIA Linux kernel module lets an unprivileged container user escape to root on the host.

Main Stage·37 min
Can Ozian · Kagan Capar
Follows a mistriaged PHP fuzzer crash from a core Zend use-after-free to a command run on stock PHP despite ASLR and disable_functions.
Main Stage·44 min
Alelsandr Krasnov
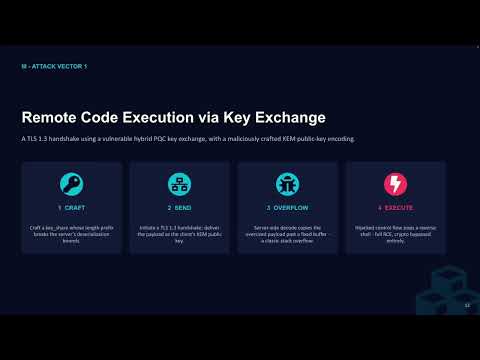
Shows how memory corruption, compiler-introduced timing leaks, and fault injection can break post-quantum ML-KEM and ML-DSA implementations today, without a quantum computer.