How I Met Your Printer
Where
PasswordsCon
BSides Las Vegas
Duration
44 min
Shows how office printers leak stored credentials that can be used to move deeper into a corporate network.
Summary
Tom Pohl, a penetration testing team manager, argues that office printers are a common and overlooked way into corporate networks. Many of the printers he meets during internal tests still use default credentials, and when those fail he looks for other routes, such as a hidden supervisor account with a blank password on some Ricoh models.
The talk walks through several pass-back techniques, where the device is tricked into sending its own stored credentials to an attacker-controlled listener. Examples include pointing the LDAP address lookup setting at a fake server and using the built-in test button, and changing the SMTP server and enabling automatic email alerts so the printer sends its mail login out. Scan-to-folder settings can be redirected to an attacker-controlled share to capture NTLMv2 hashes, which can then be cracked offline. Stored SMTP credentials were also shown to grant access to a mailbox holding scanned documents from across an organization. The talk also covers similar weaknesses in server management interfaces and room control systems.
For defenders, the recommendations are to segment management interfaces, change every default account, require encrypted authentication, use app-specific passwords or tightly scoped service accounts, and forward device logs to a central logging system. Tom closes by noting that any networked device storing credentials can be exposed in the same way.
Related talks

PasswordsCon·43 min
John-André Bjørkhaug
Shows how RFID access badges fail through default keys, cloning and replay attacks, drawn from physical penetration tests.
Radio Frequency Village·29 min
Greg
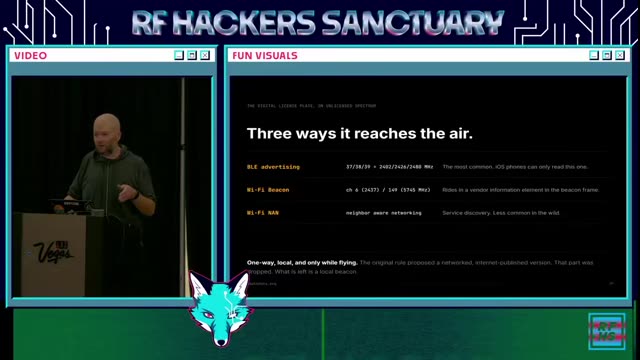
Explains how drones appear on the RF spectrum, how Remote ID and DJI control links can be detected and decoded, how they can be spoofed or replayed, and where RF sensing falls short.

PasswordsCon·24 min
Walks through hunting CVEs in Wi-Fi routers using open-source research and the risks of default configurations.