Daniel Romero - Why You Should Fear Your Mundane Office Equipment
Demonstrates persistent backdoors and network pivots achievable through common office equipment including printers, scanners, and VOIP phones.
Summary
Office Equipment as Attack Infrastructure
Daniel Romero presents research on security vulnerabilities in mundane office equipment — printers, multifunction devices, IP phones, and network-attached scanners — showing how attackers use these devices as persistent staging points.
Printer Exploitation
Enterprise laser printers from major vendors run full embedded Linux with web management interfaces. Romero demonstrates unauthenticated remote code execution in HP, Xerox, and Lexmark management portals, providing persistent access that survives endpoint security agent deployment.
Print Job Interception
Beyond code execution, printers that spool jobs locally allow attackers to intercept, copy, and exfiltrate sensitive printed documents including M&A communications, HR records, and legal filings.
Network Pivoting Through IoT
Office IoT devices (HVAC controllers, badge readers, digital signage) run stripped-down embedded Linux with minimal security and provide network footholds on VLANs that corporate workstations cannot directly access.
Related talks

Main Stage·40 min
Reynaldo · nyx
Reverse engineers commercial vape and sound monitoring sensors installed in school restrooms, uncovering unauthenticated telemetry feeds and cloud vulnerabilities.

Main Stage·42 min
Mark Omo · James Rowley
Reverse engineers electronic gun safes and commercial digital vaults, demonstrating effortless physical and electromagnetic bypasses across leading brands.
Main Stage·40 min
Dennis Giese · braelynn
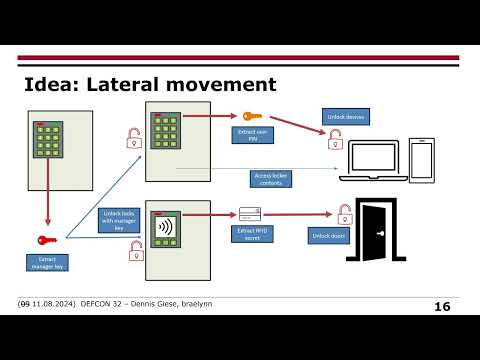
Security evaluation and hardware attack surface analysis of smart electronic lockers and storage cabinets.