Bill Swearingen - HAKC THE POLICE
Exposes persistent plaintext transmission failures in P25 public safety radio networks used by law enforcement and first responders.
Summary
P25 Public Safety Radio Vulnerabilities
Bill Swearingen (Security Consultant, ICSDefense) revisits and extends prior research on Project 25 (P25) digital radio networks used by US law enforcement, federal agencies, and first responders, demonstrating that years-old interception vulnerabilities persist.
P25 Encryption Failures
P25 radios support encryption (DES-OFB, AES) but deployment is inconsistent. Many agencies transmit plaintext by default, allowing passive monitoring with commodity RTL-SDR hardware and open-source P25 decoders (OP25, DSDPlus).
Encryption Status Indicator Bypass
Even when encryption is intended, officers can accidentally transmit in the clear if the encryption indicator is disabled by misconfiguration or radio malfunction. Swearingen documents cases of sensitive operational communications intercepted in cleartext during active law enforcement operations.
Strike Attack on Encrypted P25
Using an IMSI-catcher-like approach adapted for P25, Swearingen demonstrates a downgrade attack that causes encrypted radios to fall back to analog, enabling passive interception of sensitive tactical communications.
Related talks

Main Stage·40 min
Cooper Quintin · Yomna Nasser
Shows how modifying an inexpensive consumer 4G LTE mobile hotspot allows researchers to capture raw network packets and detect IMSI catcher surveillance.

Main Stage·23 min
Alan Meekins
Investigates fixed-address Bluetooth Low Energy beacons in law enforcement gear, body cameras, and consumer IoT, demonstrating long-term tracking.
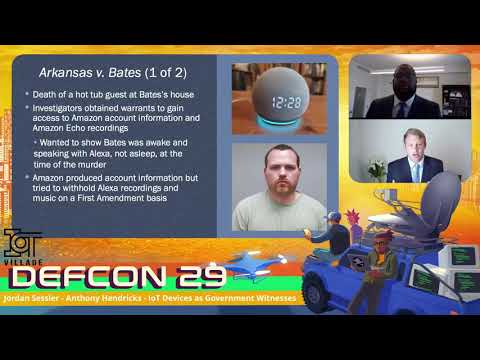
IoT Village·37 min
Stephen Sessler · Matt Hendricks
Stephen Sessler and Matt Hendricks examine how law enforcement uses consumer IoT data (Fitbits, Amazon Echos, smart appliances) as courtroom evidence.