RE for the Rest of Us: An Introduction to Reverse Engineering
Introduces reverse engineering fundamentals using hands-on Arduino hardware and Ghidra binary analysis demos.
Summary
In this practical workshop from the Blacks in Cybersecurity Village at DEF CON 33, cybersecurity researcher Sydney Johns presents an accessible guide to reverse engineering embedded firmware and compiled software binaries. Opening at 00:00, Sydney demystifies the field, reassuring beginners that reverse engineering does not require a computer science degree or mastery of complex assembly language.
At 06:04, Sydney guides attendees through interpreting microcontroller hardware datasheets to identify pinouts, memory configurations, and communication buses. At 12:00, she demonstrates hardware verification using a digital multimeter in continuity mode to trace circuit connections on target printed circuit boards. Moving to software analysis at 18:01, she contrasts high-level source code, compiled assembly instructions, and raw binary representations.
At 24:06, Sydney uploads firmware to an Arduino test board, showing how to extract binary images and load ELF files into disassembly tools. At 32:00, she demonstrates navigating decompiled functions, inspecting control flow graphs, and searching for hardcoded credentials, providing attendees with a reproducible methodology for foundational hardware reverse engineering. (AI summary — Gemini Flash)
Related talks

Main Stage·43 min
Yaniv Balmas · Lior Oppenheim
Yaniv Balmas and Lior Oppenheim demonstrate reverse engineering KVM switch firmware, subverting the 8051 microcontroller to install an undetectable, persistent hardware keylogger.
Main Stage·38 min
Joseph Gabay
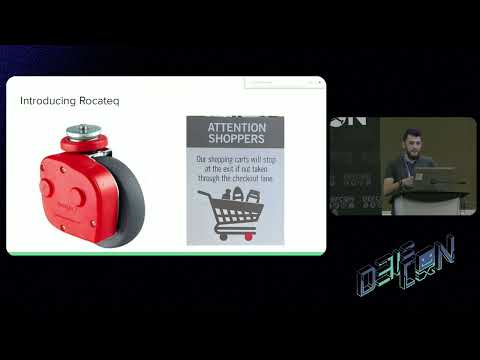
Reverse engineers electronic shopping cart containment wheels, capturing ultra-low-frequency and 2.4 GHz RF signals to unlock wheel braking mechanisms.

Village Interviews·9 min
The DEF CON Video Team gets the full overview of hands-on hardware labs, firmware analysis, and microelectronics at the Embedded Systems Village.