Backdooring Git
John Menerick explores attack vectors against Git source control workflows, demonstrating malicious hook injection and commit metadata spoofing.
Summary
Architecture and Background
Join us for a fun-filled tour of source control management and services to talk about how to backdoor software. We will focus on one of the most popular, trendy SCM tools and related services out there – Git.
Vulnerability Analysis
Nothing is sacred. Along the way, we will expose the risks and liabilities one is exposed to by faulty usage and deployments.
Exploitation and Demonstrations
When we are finished, you will be able to use the same tools and techniques to protect or backdoor popular open source projects or your hobby project. John Menerick works on Security @ NetSuite.
Remediation and Defensive Strategies
John’s interests include cracking clouds, modeling complex systems, developing massive software-defined infrastructures, and is the outlier in your risk model.
Related talks

Main Stage·38 min
Maksim Shudrak
Provides an insider breakdown of detecting and neutralizing the historic XZ Utils backdoor (CVE-2024-3094) before widespread Linux distribution deployment.
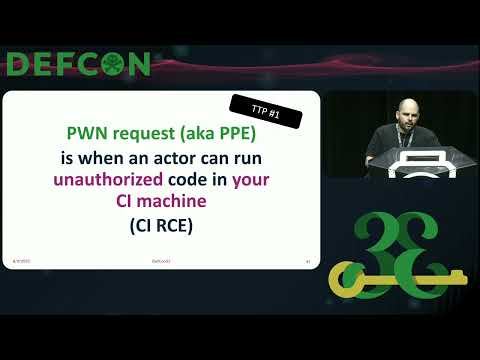
Main Stage·42 min
Aviad Hahami
Reconstructs the multi-stage CI/CD supply chain compromise of the popular tj-actions GitHub Action, detailing secret exfiltration and attacker tradecraft.
Main Stage·38 min
Maksim Shudrak
Provides an in-depth breakdown of discovering and neutralizing the historic XZ Utils backdoor (CVE-2024-3094) before stable Linux distribution deployment.