Talks·16 min
Remi Seguy
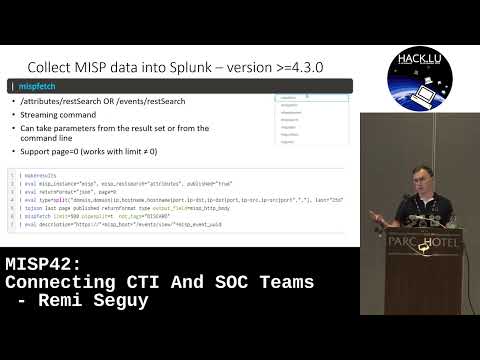
Shows how a Splunk app pulls MISP indicators into log searches and pushes findings back to the threat-sharing platform.
intelligencethreat-detectionsecurity-operations+2
DEF CON 34 talks are here: 354 talks, summarized and searchable.
Browse DEF CON 341 talk in the archive.
1–1 of 1 talk
Talks·16 min
Remi Seguy
Shows how a Splunk app pulls MISP indicators into log searches and pushes findings back to the threat-sharing platform.