Talks·48 min
Luke McOmie
Argues that enterprise security should run as a continuous, business-driven program rather than annual checkbox testing.
managementrisklessons-learned+2
DEF CON 34 talks are here: 354 talks, summarized and searchable.
Browse DEF CON 34Richmond, VA, USA · June 2023 · 25 talks
Talks from RVAsec 12 (2023).
1–24 of 25 talks
Talks·48 min
Luke McOmie
Argues that enterprise security should run as a continuous, business-driven program rather than annual checkbox testing.
Talks·49 min
Scott Small
Shows how ransomware and malware families change their behaviors over time and how TTP intelligence helps defenders keep pace.
Talks·51 min
Dan Han
Explores how a university security leader reshaped access controls around identity and device signals after the pandemic.
Talks·46 min
Fletcher Davis
Explains how red teamers can tailor offensive tradecraft to a target's environment so their activity blends in with normal behavior.
Talks·47 min
Jason Wonn
Shows how to run tabletop incident response exercises at work using Dungeons and Dragons style facilitation and planning.
Talks·54 min
Aliscia Andrews
Virginia's deputy homeland security secretary explains the state's cyber roles, workforce pipeline, and why incidents must be reported.
Talks·50 min
Andrea Matwyshyn
Explains how courts, regulators and corporate law already hold software makers liable for security failures.
Talks·50 min
Josh Cigna
Explains how passkeys replace passwords, sync across devices, and resist phishing, with a live registration demo.
Talks·49 min
Qasim Ijaz
Walks through Active Directory pentest techniques that abuse default Windows features, from name resolution poisoning to Kerberoasting.
Talks·42 min
David Girvin
Explores where ChatGPT adds value to security roles like threat modeling and reporting, and where it fails or gets jailbroken.
Talks·49 min
Kevin Massey
Builds a userland heap allocator step by step and shows how its design flaws can be exploited.
Talks·51 min
Adrian Amos
Traces the history of passwords and walks through MFA and passwordless options in Azure AD conditional access.
Talks·38 min
Colin Estep
Shows how behavioral analytics and DLP signals reveal employees moving corporate data to personal cloud apps before leaving.
Talks·1 hr 3 min
Andy Ellis
Argues everyone leads and offers practical habits on wellness, inclusion and alignment to stop wasting team energy.
Talks·50 min
Rick Lull
Surveys network protocols, foundational security controls, and how SASE and ZTNA fit into modern remote-access designs.
Talks·52 min
Denis Mandich
Explains how quantum computers threaten current encryption and what post-quantum and key distribution options can do about it.
Talks·47 min
Drew Schmitt
Shows how ransomware groups rebrand to dodge law enforcement and how analysts link new identities back to older groups.
Talks·45 min
Brendan O'Leary
Traces how a Shakespeare cipher project led a code-breaker into wartime cryptanalysis and the origins of the NSA.
Talks·51 min
Andrew Hendela
Explains why component inventories miss supply chain attacks and how tracking software behavior can close the gap.
Talks·50 min
Ian MacRae
Explains NIST 800-171 and CMMC requirements for businesses handling federal contract information, from scoping to audits.
Talks·48 min
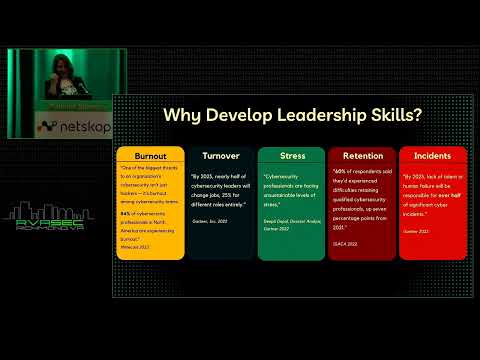
Kate Collins
Presents a leadership creed for info-sec professionals, using The Mandalorian to illustrate principles for leading people and teams.
Talks·40 min
Mark Arnold
Walks through five recurring security gaps seen across client engagements and how to map them to a framework.
Talks·43 min
Dwayne McDaniel
Explains honey tokens as decoy credentials that raise alarms when intruders use them, with AWS build examples and tool options.